Access controls
Permissions and tenant boundaries are intended to restrict what people, assistants, and integrations can see or do.
TRUST
Technology should help your organization make decisions—not take away its authority, visibility, or accountability.
WHY TRUST MATTERS
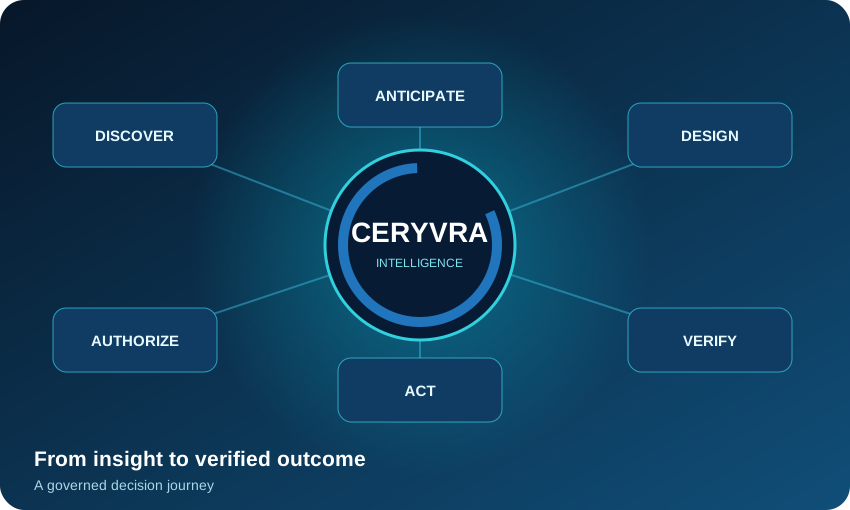
Ceryvra is designed around a simple principle: important decisions and automated actions should be explainable and accountable. Organizations need to know which information informed a recommendation, who was authorized to approve an action, what was executed, and what evidence supports the outcome. The intended architecture separates proposals from permissions, actions from results, and monitoring from independent verification.
Permissions and tenant boundaries are intended to restrict what people, assistants, and integrations can see or do.
Evidence, approvals, actions, and checks should be traceable through the decision lifecycle.
SECURITY FOUNDATION
Governance is part of the decision process, not an afterthought.
Give people and integrations only the access they are authorized to use.
Require policy checks, limits, and approvals before supported actions.
Maintain traceable records of inputs, decisions, permissions, and outcomes.
Check whether an action actually achieved its intended result.
CONTROL IS BUILT INTO THE PROCESS
Permissions and policies determine what the platform may access or recommend. Supported actions require the appropriate authority, and evidence provides a basis for independent review.
Explore technical safeguards